~/ whoami
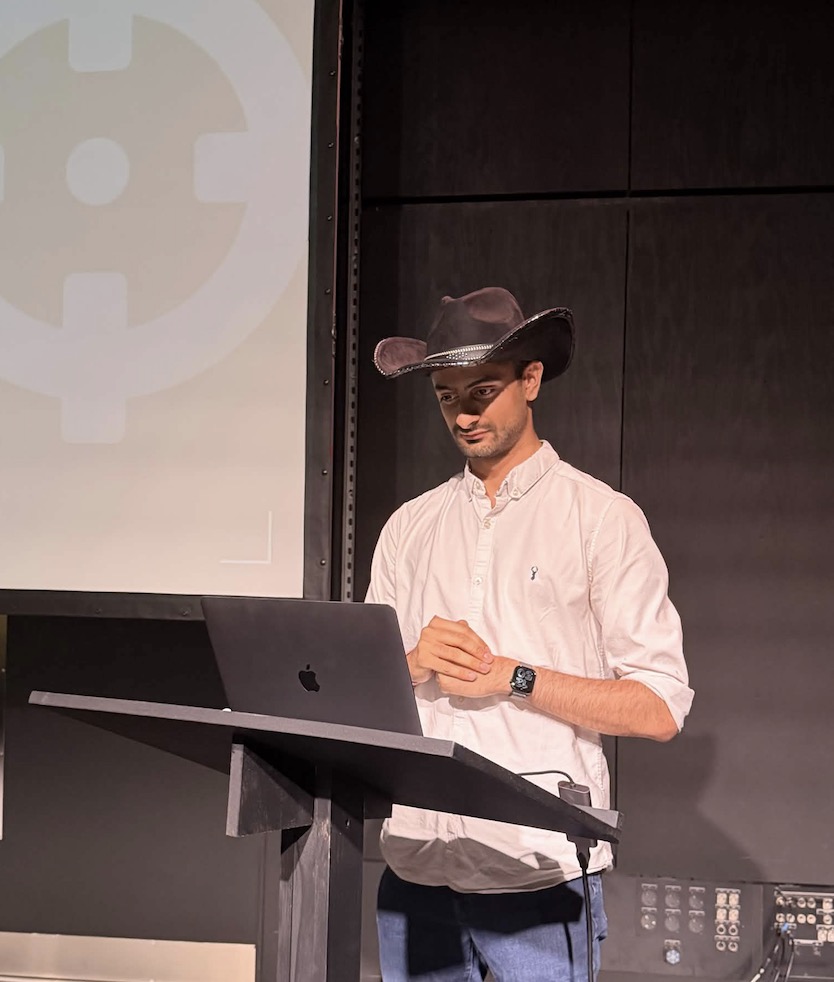
Rishi — @rxerium speaking on stage

about rishi

Vulnerability researcher and threat intelligence specialist based in London, UK. Security Researcher at The Shadowserver Foundation and part of the executive leadership of the UK OSINT community.

profile

Rishi is a vulnerability researcher and threat intelligence specialist working at the frontline of cyber defence, with detection research recognised by governments across North America, Europe, and Asia, and trusted by national cyber authorities and law enforcement to help identify and counter emerging threats.

He has briefed the UK Government and Policy Makers on the risks confronting critical infrastructure and the software supply chain. A multi-time DEF CON and BSides speaker, he has also presented at OWASP London and shared his perspective with senior audiences on the fast-evolving threat landscape.

A significant part of his work is committed to the open-source community, authoring detection tooling relied upon by others and contributing to the frameworks behind modern reconnaissance and attack surface discovery. He gives his time to help defenders worldwide and to produce educational content and events for those looking to learn.

His broader background spans enterprise IT, endpoint security, compliance, and infrastructure, giving him a grounding in both the technical detail and the wider operational picture.

experience

The Shadowserver FoundationSecurity Researcher
Jan 2026 — Present
  • Engineering detection signatures and internet-wide scans
  • Turning honeypot data into actionable detections
  • Supporting government cyber response
  • Equipping CSIRTs with exposure data
UK OSINTExecutive Leadership
Mar 2025 — Present
  • Strengthening sovereign UK intelligence capability
  • Produces high-quality OSINT educational content
  • Organises and hosts OSINT events across the UK
KYNDSenior Security Researcher — London
Feb 2022 — Aug 2026
  • Led enterprise vulnerability research
  • Architected an internet-wide platform scanning millions of assets
  • Authored advisories translating CVE, CVSS and EPSS data into business risk
ECCFirst Line Support Engineer
Jan 2020 — Aug 2021
  • Delivered network and endpoint support within SLA across 500 customers
  • Led Windows 10 migration and MFA rollout to 2000 endpoints
  • Maintained EPP/MDR, Active Directory and O365 / Google Workspace

affiliations

ProjectDiscovery Pioneer
Oct 2024 — Present
  • Authored 950+ Nuclei detection templates used worldwide
  • Shapes PD Cloud through beta testing and product guidance
  • Authors technical blog content for ProjectDiscovery
OWASP Member
Feb 2025 — Present
  • Contributes to Amass, OWASP's attack surface framework
  • Contributes to Nettacker, an automated recon framework
  • Supported the OWASP Amass workshop at DEF CON 33

recognition

government & certs · 7 citations
UKNCSC (UK Government)
Recognised detection script for GoAnywhere MFT exploitation.
CVE-2025-10035
PLCERT Polska
Adopted detection scripts into Artemis tooling.
CVE-2025-49113CVE-2025-68461
CACalifornia Cyber Security Integration Center
Cited detection in an official cyber advisory.
CVE-2025-10035
USNIST / NVD
Featured detection script on the official advisory page.
CVE-2023-40000
ESSpanish Government Agency (INCIBE)
Referenced detection script in national guidance.
CVE-2023-40000
LUCIRCL (Luxembourg)
Referenced vulnerability research across advisories.
research
VNGov. of Vietnam
Cited detection work in national advisories.
advisories
CTFBSides Las Vegas · Aug 2025
Won the ProsVJoes capture-the-flag competition.
winner
industry · press · media
INVendor citations
Detection research cited across vendor advisories and threat reports.
SonicWall Censys Black Kite QualysReSecurityCoalitionIntruderFeedlyPT SecurityDarkWebInformer
PRPress coverage
Press and news coverage from across the internet.
AUPodcasts & newsletters
Research discussed on air and in leading security briefings.

research

blogs

projects

Open-source tooling, detection content and research — built and maintained on GitHub.

detection & threat intel osint & workflows upstream contributions
disclosed cves · 11 total full cve stats ↗
11
disclosed CVEs
3
critical · CVSS 9.8
8
high · CVSS 7.5
7
years · 2015–2026
by severity
  • 3 Critical (27%)
  • 8 High (73%)
by year
  • 4 · 2023
  • 2 · 2024
  • 1 · 2026  1 · 2021  1 · 2019
  • 1 · 2017  1 · 2015
by class
  • 5 SQL injection (45%)
  • 4 Traversal / file read (36%)
  • 1 SSRF (9%)
  • 1 RCE (9%)
showing 3 of 11
CVE-2026-890262026
criticalCVSS 9.8
Issabel Framework / Issabel PBX
hardcoded JWT key → RCE
Identical hard-coded HS256 JWT signing key across every install allows unauthenticated attackers to forge bearer tokens and invoke the manager originate endpoint for remote command execution. Exploited in the wild.
cve.org CWE-321
CVE-2023-543992023
criticalCVSS 9.8
Hongjing e-HR < 8.2
SQL injection · unauthenticated
UNION SELECT injection via the categories parameter on /servlet/codesettree exposes arbitrary database content including credential tables.
cve.org CWE-89
CVE-2023-544002023
criticalCVSS 9.8
Fumasoft Fumeng Cloud
SQL injection · unauthenticated
UNION-based injection through the Name parameter of the getEmpByname action on AjaxMethod.ashx against a MSSQL backend — read and modify database contents.
cve.org CWE-89
CVE-2024-583882024
highCVSS 7.5
Sharp / Toshiba Tec MFPs
local file inclusion
Directory traversal via the path parameter on installed_emanual_down.html reads arbitrary files outside the manual directory.
cve.org CWE-22
CVE-2024-583872024
highCVSS 7.5
Inspur Haiyue HCM Cloud
arbitrary file read
Unvalidated index / ext parameters on /api/model_report/file/download traverse the filesystem and disclose sensitive files such as /etc/passwd.
cve.org CWE-22
CVE-2023-544032023
highCVSS 7.5
Yonyou U8 CRM < V16.5 / V18
arbitrary file read · auth bypass
DontCheckLogin=1 bypass plus unvalidated filePath on /ajax/getemaildata.php reads config files and other sensitive paths outside the web root.
cve.org CWE-22
CVE-2023-544022023
highCVSS 7.5
iDocView
SSRF → local file read
Hard-coded default token (testtoken) bypasses auth on /doc/upload; unrestricted URL schemes including file:// expose local OS and app files.
cve.org CWE-918
CVE-2021-480082021
highCVSS 7.5
Chanjet CRM
SQL injection · unauthenticated
UNION-based injection via the site_id parameter on the webservice endpoint extracts sensitive data from the backend database.
cve.org CWE-89
CVE-2019-257762019
highCVSS 7.5
Weaver E-cology
SQL injection · unauthenticated
UNION injection through userIdentifiers on the mobile plugin endpoint, bypassing space-based filters to dump admin credentials and sensitive rows.
cve.org CWE-89
CVE-2017-202842017
highCVSS 7.5
Caucho Resin (resin-doc)
path traversal
Relative-path input through inputFile on the jndi-appconfig tutorial servlet reads arbitrary files outside the documentation webapp.
cve.org CWE-22
CVE-2015-201222015
highCVSS 7.5
Seeyon A6 OA
SQL injection · unauthenticated
UNION injection via attach_ids on downloadAtt.jsp dumps arbitrary database content with no authentication required.
cve.org CWE-89

speaking

Multi-time DEF CON speaker across the Red Team, Recon and Social Engineering Villages — including workshops and roundtables — alongside the BSides circuit in Europe and the US, OWASP London, Hack Glasgow and ElbSides Hamburg, plus a ProjectDiscovery interview and a Current State of AI roundtable in Budapest. He has also briefed the UK government and policymakers on supply chain risk and vulnerability research.

20+total sessions
2workshops
8countries
1delivered · SecTor
talks by year · 20+ total
20254
202615
las vegas · usa · 4 sessions
DEF CON Villages

Hiring-machine social engineering, DNS OSINT and Amass — talks plus hands-on workshops.

Red Team VillageRecon VillageSE Village ×2
europe + us circuit · 8 stops
BSides circuit & OWASP

AI-driven vulnerability research, OSINT and attack surface management.

Las VegasCymruPortoPragueBudapestLuxembourgOWASP LondonHack Glasgow
policy + community · 3 sessions
Briefings, interviews & roundtables

Supply chain risk and vulnerability research for critical infrastructure.

UK Government BriefingProjectDiscovery interviewCurrent State of AI roundtable
latest · deliveredSecTor 2026 — Toronto, Oct 6–8Ghost in the Hiring Machine — alongside DEF CON, BSides and Hack Glasgow appearances.

skills

domains
vulnerability research threat intelligence detection engineering osint attack surface management supply chain security internet-wide scanning phishing detection AI security public speaking mentoring
tooling & techniques
nuclei amass nettacker shodan dns osint certificate transparency go cve / cvss / epss analysis honeypots signature development

Want the full CV?

Open to security collaborations, speaking engagements, and media commentary.

request cv